AI in Cyber Security and Ethical Hacking | A 40 Hour Winter Bootcamp Program'26
About the event
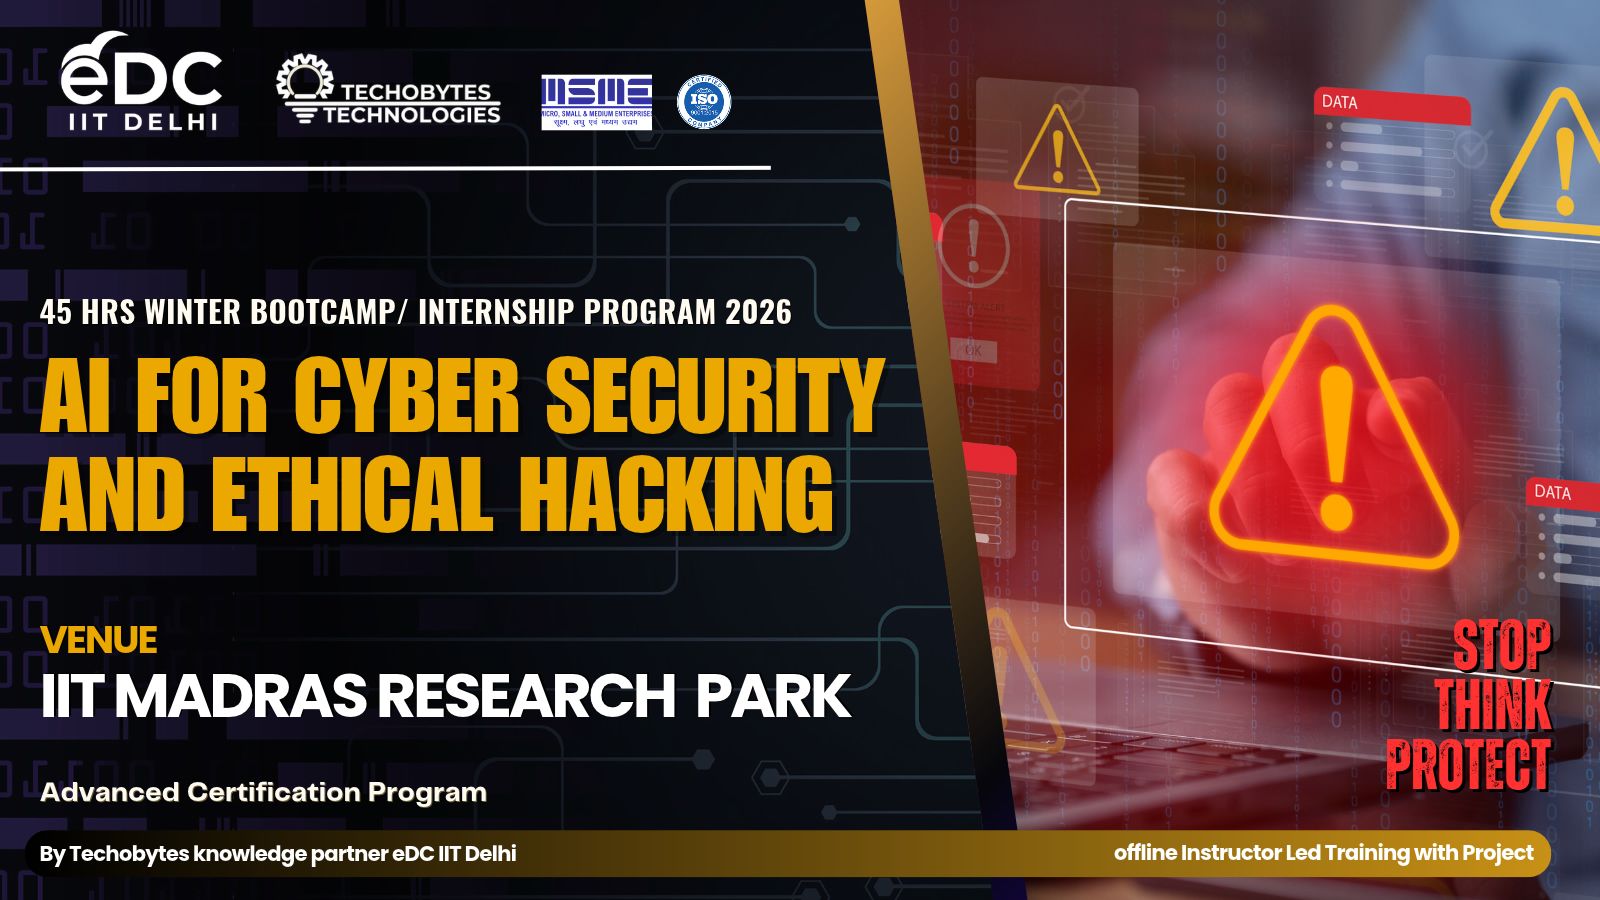
40 hour winter bootcamp/internship program 2026 with project at IIT Madras Research Park by Techobytes in collaboration with EDC IIT Delhi.
About Techobytes:
Techobytes Technologies is recognised as a leading expert in the design and delivery of technical, soft and hard skills training from individual courses and seminars to certification programs and full-scale training solutions, from classroom training to online training.
Duration: The event is scheduled for 5 consecutive days, from 22 December 2026 to 26 December 2026.
Training Time: 10:00 AM – 5:00 PM, Daily
The training will include 40-45 hours of intensive learning with a project, covering concepts from basic to advanced level.
Benefits and certification:
40-45 hours certification/internship program.
3 certificates in each training. Participation Certificate + Recommendation/Internship Certificate + Project Completion Certificate.
Updated industry-equipped curriculum.
Work on live projects.
Hands-on training by certified trainers from the industry.
Complimentary resume and CV building session.
Get an opportunity to attend a technical workshop from Techobytes in IIT’s.
Level: Beginner to Advanced
Open to ALL, B.tech, B.E, B.sc IT, M.sc IT, IT Sector, Programmers, Undergraduate students, early researchers, or professionals entering into Cyber domain or want to make their career in the same.
Cyber security & ethical hacking:
Module 1: Cyber security foundations
Cyber Security landscape & modern threats
Ethical Hacking methodology & frameworks (CEH, OWASP, MITRE ATT&CK)
Types of hackers & attack surfaces
Introduction to AI in Cyber Security
Module 2: Footprinting & reconnaissance (advanced)
Active & Passive reconnaissance
OSINT (Open Source Intelligence) tools
AI-powered reconnaissance techniques
Tools: Maltego, Recon-ng, Shodan
Module 3: Network scanning & enumeration
Advanced Nmap scanning & scripting (NSE)
Service & vulnerability detection
Enumeration techniques (users, shares, DNS, SNMP)
Hands-on: Network mapping & analysis
Module 4: System hacking & privilege escalation
Password cracking (modern techniques)
Credential attacks (brute force, dictionary, rainbow tables)
Privilege escalation (Windows/Linux)
Post-exploitation techniques
Module 5: Malware & threat analysis
Viruses, worms, trojans, ransomware
Malware analysis basics (static & dynamic)
AI-based malware detection
Botnets & modern cyber threats
Module 6: Sniffing, MITM & network attacks
Packet sniffing & analysis (Wireshark)
Man-in-the-Middle (MITM) attacks
Session hijacking techniques
Secure communication practices
Module 7: Social engineering & human hacking
Phishing, spear phishing, vishing
Social engineering toolkit (SET)
AI-driven phishing attacks & deepfakes
Defense strategies
Module 8: Web application security (modern OWASP Top 10)
SQL Injection (manual + automated)
Cross-Site Scripting (XSS)
Command injection & CSRF
Authentication & session vulnerabilities
Hands-on: DVWA / Juice Shop
Module 9: Wireless & network security
Wi-Fi security (WPA2/WPA3 attacks)
Wireless hacking tools
Network hardening techniques
Hands-on: Wireless penetration testing
Module 10: Defense, IDS/IPS & firewalls
Firewalls, IDS/IPS systems
Honeypots & deception technologies
Log monitoring & SIEM basics
Incident detection & response
Module 11: Cloud & mobile security (updated)
Cloud security (AWS/Azure basics)
Mobile app vulnerabilities
API security
Zero Trust Architecture
Module 12: AI in cyber security (NEW – High Demand)
AI for threat detection & anomaly detection
AI-based security automation
Using AI tools for penetration testing
Adversarial AI (attacks on AI systems)
Module 13: Advanced exploitation techniques
Buffer overflow basics
Exploit development (intro)
Metasploit framework (advanced usage)
Payload creation & execution
Module 14: Penetration testing & red teaming
Penetration testing lifecycle
Red team vs Blue team concepts
Vulnerability assessment
Reporting & documentation
Module 15: Hands-on labs & real-world practice
Metasploit exploitation
Nmap advanced scanning (NSE scripts)
Network sweeping & live host detection
Windows/Linux exploitation
Password cracking (John the Ripper, Hashcat)
Wireless attacks & security testing
Web app hacking (DVWA, OWASP Juice Shop)
XSS, command injection, shell exploitation
Module 16: Cryptography & security principles
Encryption techniques (AES, RSA basics)
Hashing & digital signatures
Secure communication protocols
Real-world cryptographic applications
Module 17: Career, certifications & industry trends
Cyber Security career paths
Certifications (CEH, OSCP, Security+)
Bug bounty & freelancing
Future trends: AI security, Zero Trust, SOC
What you will get:
Hands-on labs and real attack simulations
Lab manuals & assignments
Real-world penetration testing practice
Certification and Internship Letter
Resume-ready skills
Project
Get an immersive learning experience. Sessions will be led by industry experts, offering hands-on practicals and a cutting-edge curriculum aligned with industry standards.
By attending, you'll not only gain valuable tech knowledge but also have the opportunity to network with industry professionals and connect with fellow participants, expanding both your skills and your professional circle.
- Things to know
Entry allowed for ages 16 and above
Tickets required for ages 16 and above
Pets are not allowed
Event will be held in English